Skip to content

Services, Wiki-Artikel und Blog-Beiträge durchsuchen

↑↓NavigierenEnterÖffnenESCSchließen

External CISO

Information Security Officer on demand - from EUR 1,500/month

Your certified CISO - available immediately, independent of internal hierarchies, and at a fraction of the cost of a full-time hire. Including ISMS management, NIS-2 support, and ISO 27001 certification guidance. From EUR 1,500 per month plus VAT.

ISO 27001 Lead Auditor NIS-2 expertise Available from day 1
Chris Wojzechowski, managing director of AWARE7 GmbH and point of contact for the external CISO service
External CISO / Dedicated contact
Fee
from EUR 1,500 / month plus VAT
Focus
Advisory for NIS-2, ISO 27001, critical infrastructure
Cover
Within the team, no single-person risk

Trusted by our clients

EUR per month plus VAT
from 1,500
Substitute cover during holidays and sickness
Team
Lead Auditors in the team
ISO 27001

Service Scope

What your external CISO does

Our external CISOs take on all duties of an internal information security officer - tailored to your organisation size, sector, and regulatory requirements.

01

ISMS Management

Build, maintain, and continuously improve your information security management system per ISO 27001. Documentation, risk management, and policy framework.

02

NIS-2 Compliance

Applicability analysis, implementation of the 10 mandatory measures, setup of incident reporting processes, and preparation for supervisory reviews.

03

Risk Management

Regular risk assessments, treatment of identified risks, and escalation reporting to management. Including annual management reviews.

04

Employee Awareness

Design and delivery of security awareness training. Coordination of phishing simulations and measurement of awareness development.

05

Incident Management

Assessment and management of security incidents. Coordination of responses, documentation, and reporting to relevant authorities (72-hour notification).

06

Audit Support

Preparation and support for internal and external audits (ISO 27001, NIS-2, TISAX). Coordination with certification bodies.

External vs. internal

External vs. internal CISO

A qualified internal CISO costs around EUR 100,000 to 142,000 per year including employer contributions, training and workspace, and recruiting takes months. The direct comparison shows why most mid-sized organisations choose the external model.

Criterion External CISO (AWARE7) Internal CISO
Monthly cost from EUR 1,500 plus VAT EUR 8,000-10,000
Available from Day 1 3-6 months
Coverage in absence Team coverage None
Industry breadth Multi-sector experience Single company
Certifications ISO 27001 Lead Auditor, OSCP To be organised

Our approach

How the external CISO engagement works

In five phases we take on your information security management - from initial consultation to continuous operations.

  1. 01

    Initial consultation & needs analysis

    Free intake: we clarify your industry context, regulatory requirements (NIS-2, ISO 27001, critical infrastructure), and the current state of your information security. You receive an initial assessment and a tailored proposal.

  2. 02

    Onboarding & current-state assessment

    Systematic analysis of your IT landscape, existing documentation, and organisational structures. Identification of quick wins and critical gaps. You have a dedicated point of contact from day one.

  3. 03

    ISMS build-out or enhancement

    Development or optimisation of your information security management system: risk assessment, security policy, guidelines, and procedures - scaled to your organisation size and sector.

  4. 04

    Operational management

    Your CISO in ongoing operations: assess security incidents, coordinate measures, raise staff awareness, produce regular status reports to management.

  5. 05

    Continuous improvement

    Annual management review, adaptation to new threat landscapes and regulatory changes. Audit preparation and support for internal and external reviews.

Why AWARE7 as your external CISO

What sets us apart from other providers

Pure awareness platforms don't test systems. Pure consulting firms are too far removed. AWARE7 combines both: we hack your infrastructure and train your employees: tailored to mid-sized companies, personal, without enterprise overhead.

Research and teaching as our foundation

20 %

Around 20% of our revenue comes from research projects for the BSI and the BMBF. Our studies, published at ACM and Springer conferences, analyse millions of websites and tens of thousands of phishing emails. Three of our executives are professors at German universities at the same time.

Digital sovereignty: no compromises

100 %

From first contact to final report, your data is stored on our own servers in Germany - no US cloud providers, no third-country transfers. Our AI also runs on our own hardware in Germany - with locally operated open-source models. Client and project data never reach external AI services. All staff are permanently employed, covered by social insurance and bound by uniform legal obligations.

More on digital sovereignty

Fixed price within 24h: predictable project timelines

24 h

Within 24 hours you receive a binding fixed-price quote without hourly rate risk. A well-practised team and standardised processes ensure a clear schedule with a defined start and end date.

Your dedicated contact

1:1

A personal project manager accompanies you from the first meeting through implementation. You book appointments directly with your contact person and keep the same contact throughout the project.

Peer-reviewed publications

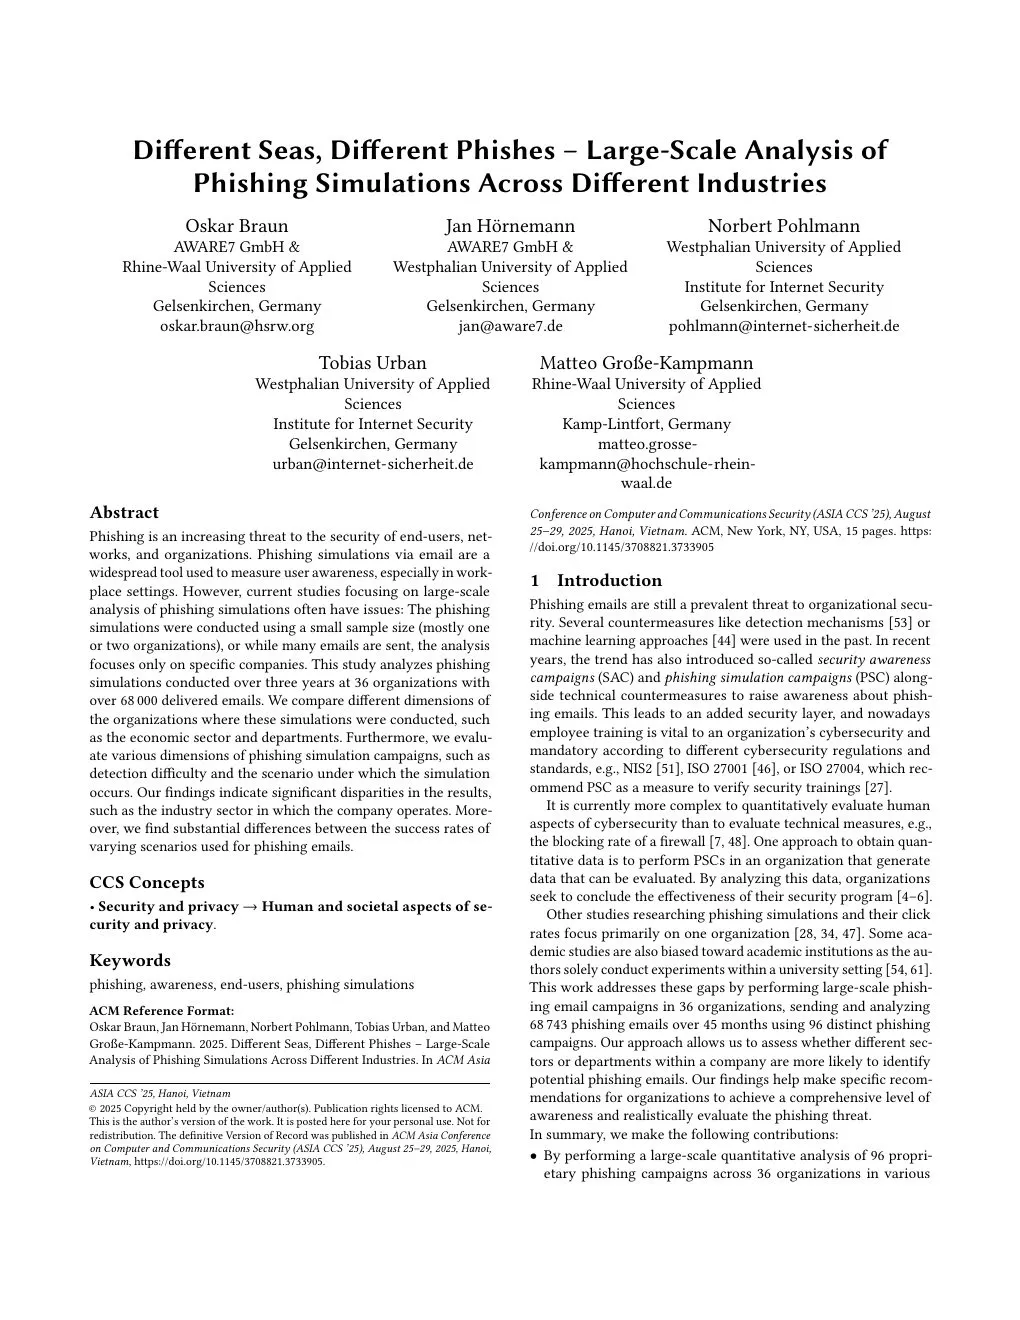
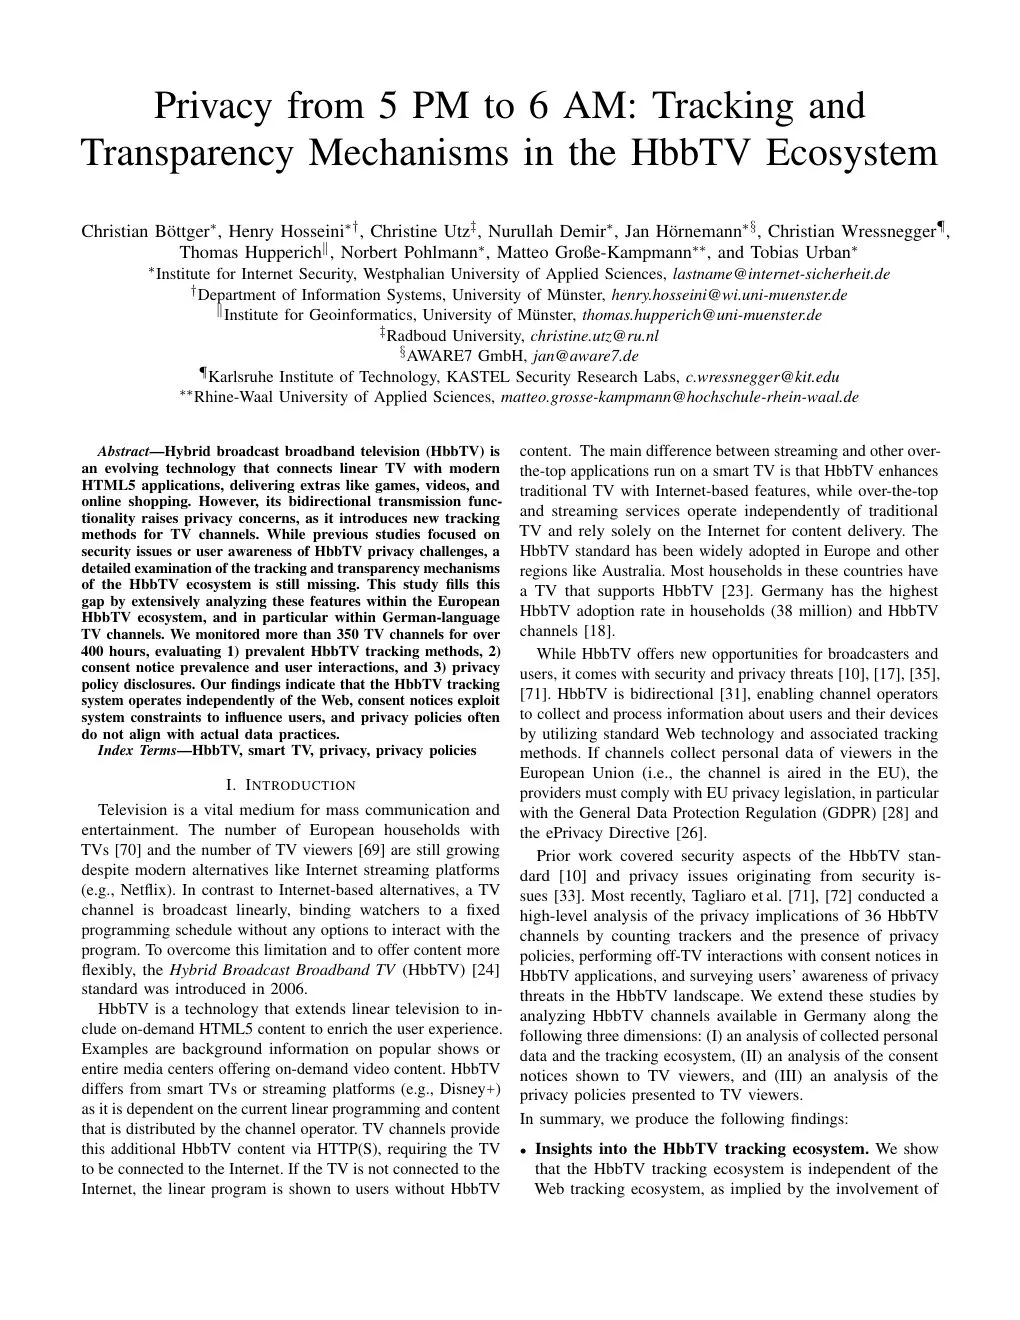
First page of the paper: Different Seas, Different Phishes - Large-Scale Analysis of Phishing Simulations

Different Seas, Different Phishes - Large-Scale Analysis of Phishing Simulations

ACM AsiaCCS 2025

Oskar Braun, Jan Hörnemann, Norbert Pohlmann, Matteo Große-Kampmann

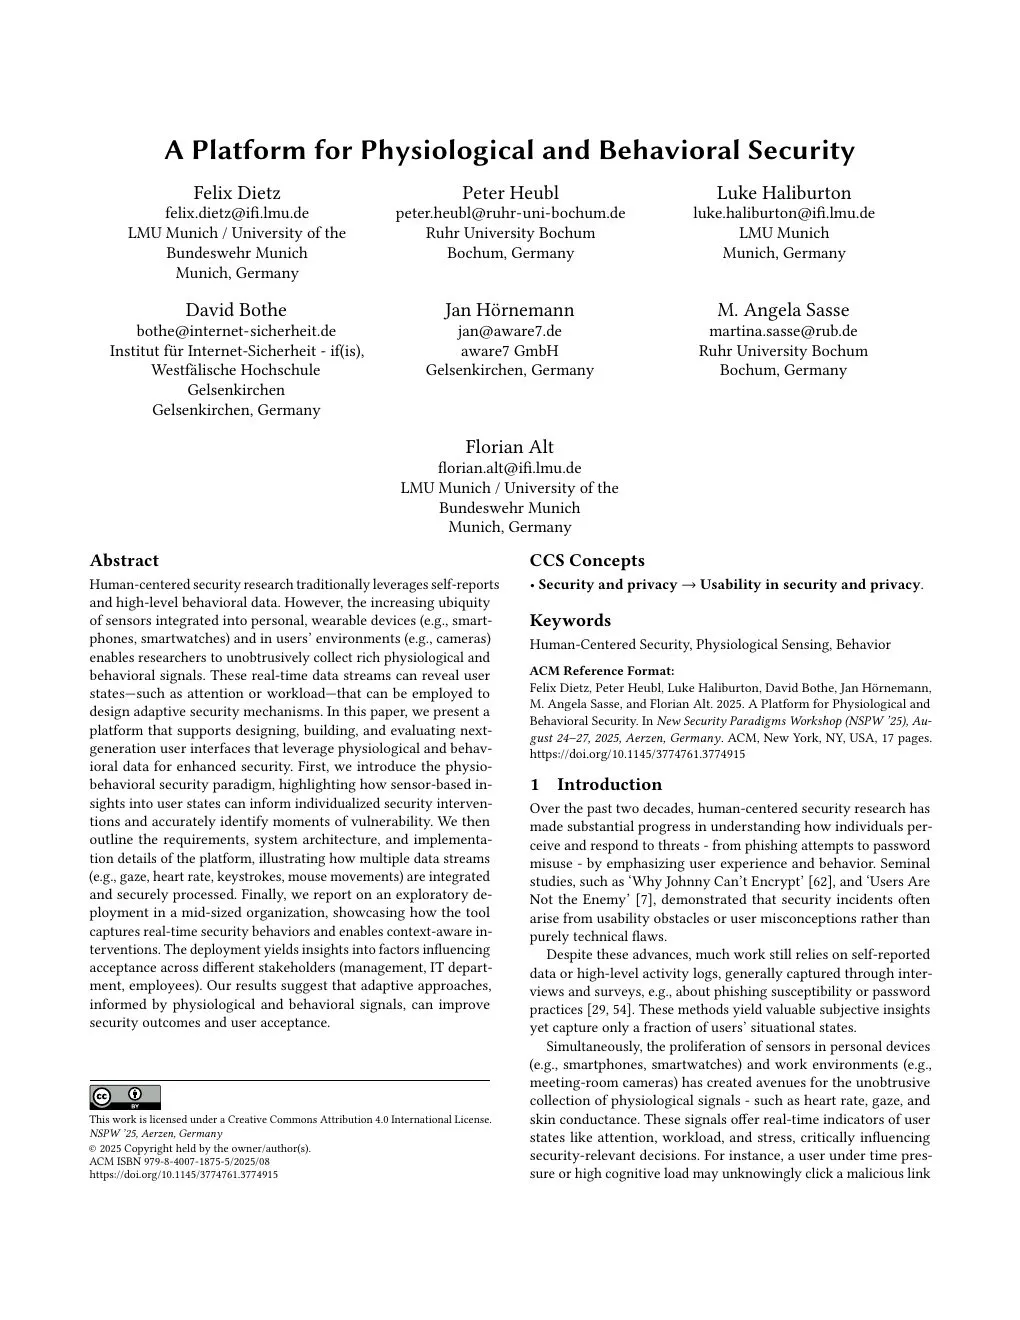
First page of the paper: A Platform for Physiological and Behavioral Security

A Platform for Physiological and Behavioral Security

NSPW 2025

Jan Hörnemann

First page of the paper: Privacy from 5 PM to 6 AM: Tracking and Transparency in the HbbTV Ecosystem

Privacy from 5 PM to 6 AM: Tracking and Transparency in the HbbTV Ecosystem

IEEE/IFIP DSN 2025

Jan Hörnemann, Norbert Pohlmann, Matteo Große-Kampmann

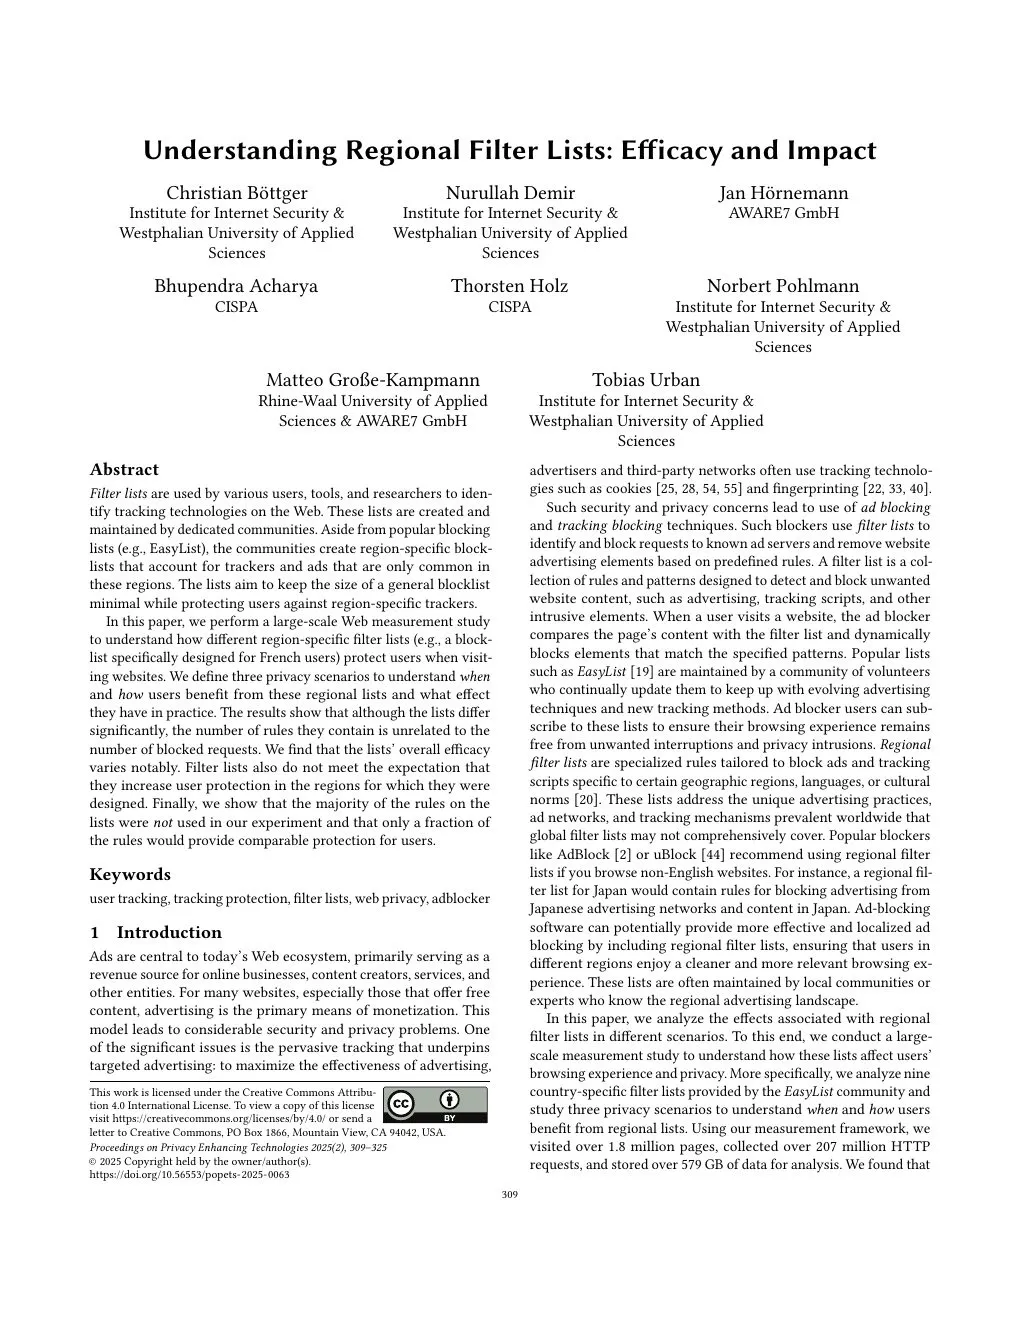
First page of the paper: Understanding Regional Filter Lists: Efficacy and Impact

Understanding Regional Filter Lists: Efficacy and Impact

PoPETS 2025

Jan Hörnemann, Norbert Pohlmann, Matteo Große-Kampmann

Who is AWARE7 the right partner for?

Mid-sized companies with 50-2,000 employees

Companies that need real security, without paying for a DAX-corporation provider. Fixed price, clear scope, one point of contact.

IT managers & CISOs

Who have to argue convincingly in-house and need a report in boardroom language for that, not just technical findings.

Regulated industries

Critical infrastructure, healthcare, financial services: NIS-2, ISO 27001, DORA. We know the requirements and deliver evidence that auditors accept.

Your external CISOs

ISO 27001 Lead Auditors with many years of ISMS experience - available from day one.

References

Reference from our ISMS consulting

These case studies are available in German.

Pricing

What the external CISO costs

No off-the-shelf packages: scope, cadence and terms are agreed in the initial consultation, matched to your organisation size, maturity and regulatory requirements.

Starting at
EUR 1,500 / month
plus VAT
Scope
agreed with you
Days per month, reporting cadence and on-site share follow your needs.
Next step
Free consultation
Request an individual quote

Frequently asked questions about the external CISO

Questions about the engagement model, costs, or collaboration? Find answers here.

The CISO is the central point of contact for all information security matters in your organisation. They develop and maintain the ISMS, advise management, coordinate security measures, train employees, and report regularly on the security status. As the interface between IT, management, and staff, they ensure information security does not remain a siloed topic.
An external CISO brings immediately deployable expertise, is independent of internal hierarchies, and costs a fraction of a full-time role. While a qualified internal CISO (including employer costs, training, and workspace) costs around EUR 100,000 to 142,000 per year, an external CISO is available from approximately EUR 1,500 per month. Additionally: they bring experience from many industries and organisations and are free from organisational blind spots.
For organisations subject to NIS-2, a designated information security officer is advisable. ISO 27001 also requires assigned responsibilities and authorities for information security. Moreover, many clients (particularly in the automotive industry, financial sector, and among critical infrastructure operators) and cyber insurers require a designated CISO. Even without a legal obligation, a CISO is the most structured solution for sustainable security management.
That depends on your organisation size, the maturity of your ISMS, and your regulatory requirements. Typical for an SME with 50-200 employees: 2-4 days per month. During the ISMS build-out phase or in preparation for certification, the effort may temporarily be higher. We scale the scope to your actual needs.
Our external CISO is available from EUR 1,500 per month plus VAT. There are no fixed packages: days per month, reporting cadence and on-site share are agreed in the initial consultation. The exact price depends on organisation size, scope, and the desired service level. For comparison: an internal full-time role costs at least EUR 100,000 per year including employer contributions and training. With an external CISO you also avoid recruitment costs, onboarding time, and the risk of staff absence.
Your external CISO is available by email, phone, and video conference. On-site appointments are arranged as needed and ensure personal contact. You have a dedicated point of contact who knows your organisation and provides long-term support. During security incidents we coordinate the necessary immediate measures and reporting obligations.
Yes, NIS-2 implementation is a core area of our CISO activities. We support with applicability analysis, building the required security measures, implementing incident reporting processes, and preparing for supervisory reviews. Our CISO service covers all NIS-2 requirements on security management.
Unlike an internal CISO, there is no single-person risk with us. There is always a qualified substitute in the AWARE7 team who knows your organisation and its structures. This is one of the major advantages of the external model over a single internal role.
Of course. We actively support the transition: knowledge transfer, documentation handover, and optional coaching of your new internal CISO are part of our service scope. Many clients start externally and build internal competence in parallel. Some also use a hybrid model where an internal coordinator is complemented by our external expertise.

Information security - without a full-time hire.

Your certified CISO is available from EUR 1,500 per month plus VAT - immediately, without recruitment costs, without single-person risk.

Free · 30 minutes · No obligation

Rufen Sie uns an

Mo-Fr, 8:00-17:00 Uhr - persönlich und unverbindlich.

0209 8830 6764
Jetzt anrufen